On-premise · Docker · No cloud account required

The AI proposes. The tool proves.

Firmlint runs deterministic static analysis on your C and C++ code, explains each finding in plain English, and proposes a fix. Every fix is re-applied to a copy of your file, re-analysed and compile-checked before you see it. Nothing is trusted without verification.

MISRA C:2012MISRA C++:2023AUTOSAR C++14CERT CCWE Top 25
finding · MISRA C:2012 Rule 21.3 p = malloc(len); AI explanation + risk Heap use in a safety-critical path can fail at runtime. ✓ Verified Finding cleared · no new findings · compiles
· Real run · header · Firmlint run header — Analysis a-1fb353de2fa9, Standard autosar-cpp14, generated 2026-10-09T15:56:21+00:00, duration 958.3s, AI review on qwen2.5-coder:14b Firmlint disclaimer — this report is a review aid, not a qualified tool under ISO 26262

How it works

Deterministic analysis. AI explanations. Proof before trust.

Standard analyzers find the issues. The AI layer helps engineers understand them. A verification loop decides which fixes are safe to show as verified.

1 · Analyze

cppcheck and clang-tidy check your code against MISRA, AUTOSAR, CERT and CWE rule sets.

→

2 · Explain

For each finding, the model writes a plain-English explanation specific to your code, a concrete risk statement, and a proposed fix.

→

3 · Verify

The fix is applied to a copy, re-analysed and compile-checked. Only fixes that pass are marked verified. The rest go to a human.

Real output · not a mockup

What an auditor receives for each finding

Every finding is exported to SARIF, HTML and JSON, with the file hash, tool versions, model name and timestamp. The screenshots below are real Firmlint runs on sample code, cropped without edits.
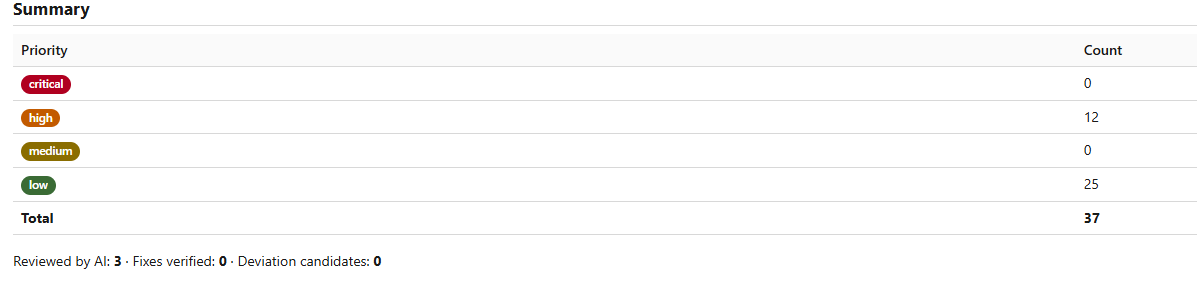
· 01 · summary · Firmlint summary — 37 findings: 12 high, 25 low. Reviewed by AI: 3. Fixes verified: 0. Deviation candidates: 0.

The summary. Notice the honest count: Fixes verified: 0. The tool doesn't claim verified work it hasn't actually verified.
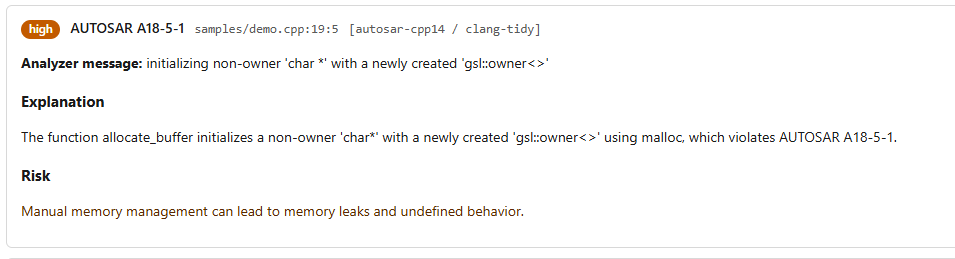
· 02 · a complete finding · Firmlint finding — AUTOSAR A18-5-1 at demo.cpp:19:5. Analyzer message: initializing non-owner char* with a newly created gsl::owner. Explanation and risk included.

Rule, location, analyzer, explanation, risk. This is the shape every finding takes.
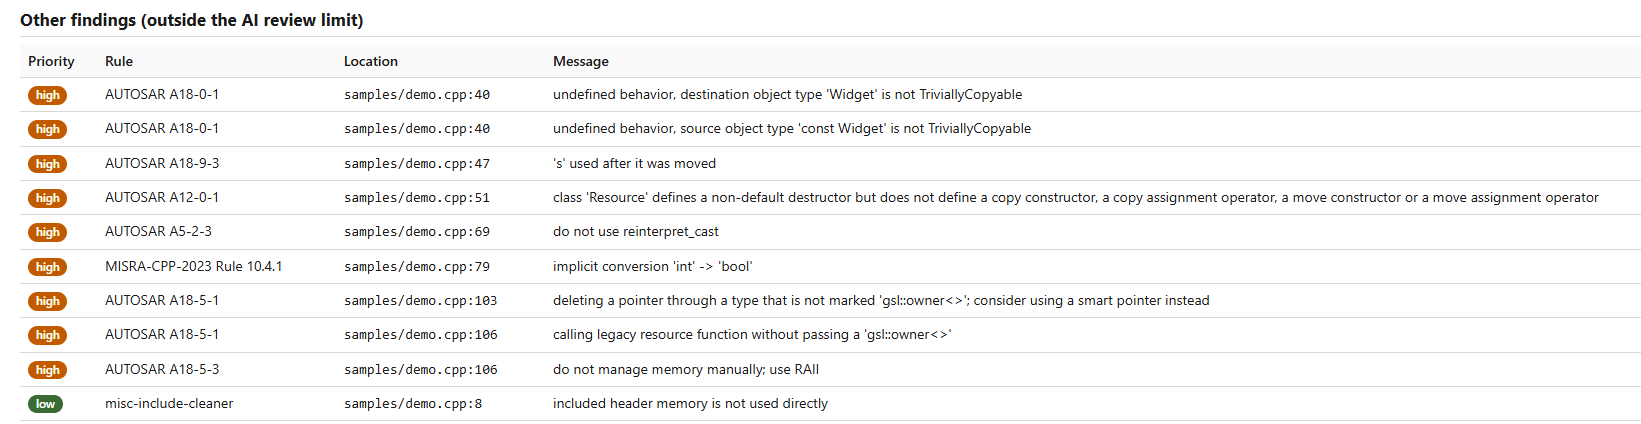
· 03 · findings outside the AI review limit · Firmlint other findings table — high and critical findings outside the AI review limit. Includes AUTOSAR A18-0-1, A18-9-3, A12-0-1, A5-2-3, MISRA-CPP-2023 Rule 10.4.1.

Findings outside the AI review limit are still reported. The tool never hides a violation — it labels what got AI review and what did not.
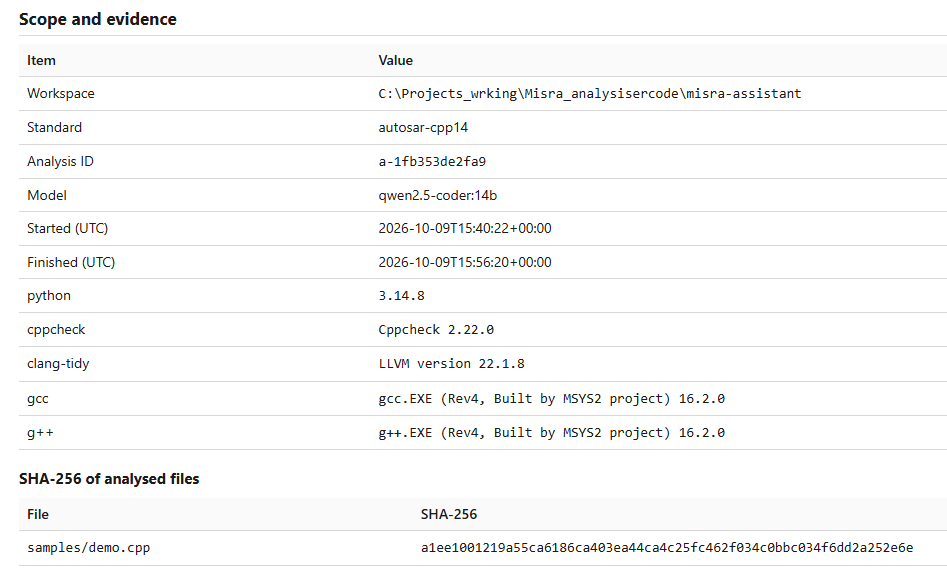
· 04 · scope and evidence · Firmlint scope and evidence — Workspace, Analysis ID a-1fb353de2fa9, cppcheck 2.22.0, clang-tidy LLVM 22.1.8, gcc 16.2.0, SHA-256 a1ee1001...

Provenance. Exact tool versions, exact timestamps, SHA-256 of every analysed file. This is what an auditor will ask to see — and most vendors don't publish it.

Why it's different

Most AI code tools trust the model. We don't.

Fixes that look right are not the same as fixes that are right. Firmlint checks each one before it reaches a reviewer.

Unverified AI suggestions

  • Accepted on how plausible they look
  • Can silence one finding and create two more
  • Often fail to compile in the real build

Firmlint

  • Re-applied to a copy of the file
  • Re-analysed with the same tool
  • Compile-checked before a verdict
  • Marked verified only when all three pass; otherwise left for a human
Coverage

Standards we check against

🚗

MISRA C:2012

Rule-based checks for C in safety-critical embedded code.

⚙️

MISRA C++:2023

Current MISRA guidance for modern C++ in automotive and industrial systems.

🧩

AUTOSAR C++14

Coding guidelines used across AUTOSAR-based software platforms.

🛡️

CERT C

Secure coding rules covering undefined behaviour and common vulnerabilities.

🔍

CWE Top 25

The most dangerous software weaknesses, mapped to your findings.

Try it now

Run it on your file. Right now.

Paste this into any terminal with Docker installed. The image is public — no signup, no account, no email required.

Terminal Public · ghcr.io
$ docker pull ghcr.io/ibrarmohammed1137/misra-assistant:latest
View package on GitHub (GitHub login required)

The deterministic layer (cppcheck, clang-tidy) runs locally. The AI layer is optional and uses local inference via Ollama by default — no code leaves your workstation.

Deployment

Runs where your code lives

Your workstation or CI runner

Ships as a Docker image. Runs on an engineer's laptop or an internal CI runner.

  • No cloud account required
  • No data leaves your network in the default configuration
  • Local inference via Ollama keeps the AI layer on-premise

Audit-ready output

Each run produces the artefacts an assessor expects.

  • SARIF for tooling and code-scanning integration
  • HTML for human review
  • JSON for pipelines and archives
  • File hash, tool versions, model name and timestamp on every finding
Pilot programme
30

days · your code · your machine

  • Success criteria agreed in writing before the pilot starts
  • Runs on your own code and infrastructure, with no data leaving your network
  • If Firmlint does not cut your review time in half, you walk away with no further obligation
Request a pilot
Request a pilot

Tell us about your project.

We'll reply within one business day. No sales call unless you ask for one.

Goes to firmlint.contact@gmail.com
